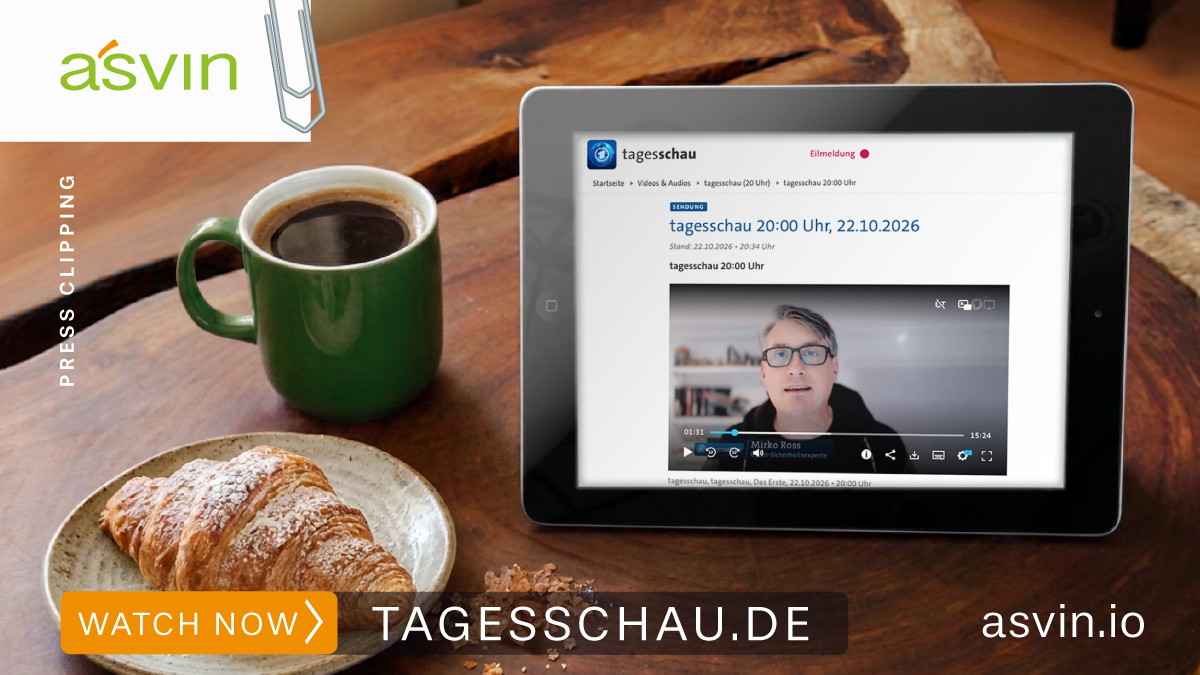
“The attacks are already in full swing”: Mirko Ross on Tagesschau about the PHP vulnerability
A critical vulnerability in the PHP programming language is affecting companies, cities, municipalities and public authorities worldwide. In an interview with Tagesschau, asvin CEO Mirko Ross explains the situation and what website operators need to do now.
Most websites run on PHP, so a large number of systems could be affected by the new vulnerability. Attackers can use it to do things like copy data from servers.
Mirko Ross says there is no time to wait:
“As we speak, the attacks are already in full swing. That is why urgent action is needed.”
What website operators need to do now
For website operators, this means two things. They should update PHP to a patched version straight away. They should also check whether attackers have already got into their systems and caused damage. An update closes the gap, but it does not undo an attack that has already happened.
According to Germany’s Federal Office for Information Security (BSI), there are currently no signs that companies or critical infrastructure have been hacked through the vulnerability. That does not mean the danger is over. Private users should also be careful, as manipulated websites may already be circulating.
Click here for the Tagesschau report:
https://www.tagesschau.de/tagesschau_20_uhr/video-1670950.html

Konrad Buck
Head of Press and Media Relations
Background & Expert Access for Media
- Detailed insights into asvin’s products and technologies
- Assessments of current cyber incidents and explanations of the security landscape
- Expert commentary and background briefings — our CEO, Mirko Ross, is a recognised expert and experienced media source on the cyber threat landscape, hacktivism, regulation and the use of AI.
I speak openly, fact-based, and without PR spin. I am a former IT journalist with decades of experience in the IT and cybersecurity space, familiar with the highs and lows of the industry. Off-the-record discussions are possible upon request.