THE CHALLENGE
Identify and assess supplier cyber risk
Detect supplier cyber risks early
Supplier cybersecurity vulnerabilities quickly become a cyber risk for companies and organizations. Threats include data leakage, unauthorized access to a company’s IT infrastructure, and malware infiltration.
asvin provides analyses of current supplier cyber risk assessments and delivers important signals for the early detection of cyber risks in the supply chain. This allows companies to implement risk mitigation measures before an unexpected cyber incident occurs at a supplier.
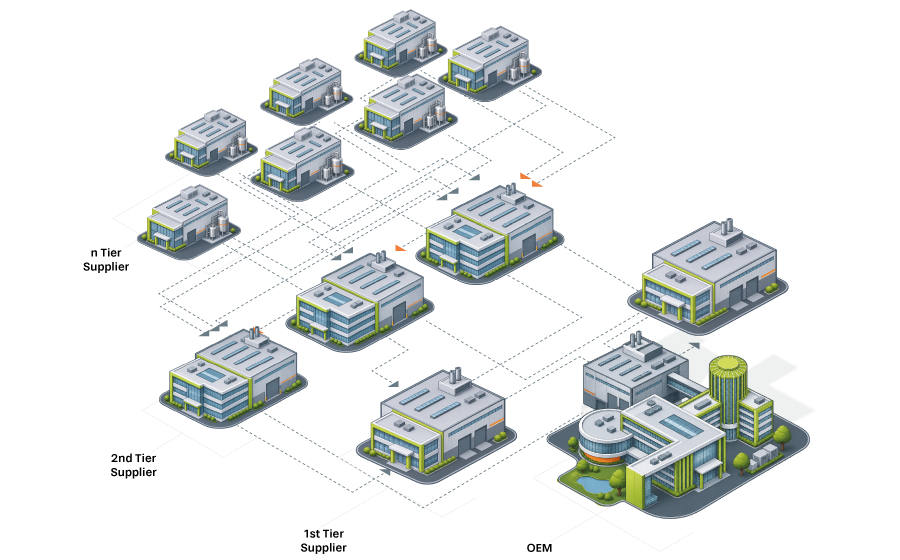
Supply chain networks are complex and constantly changing, requiring continuous assessment.
THE SOLUTION
AI-Based Cyber Risk Assessment of Suppliers
Full Visibility into Supply Chain Cyber Risks
01
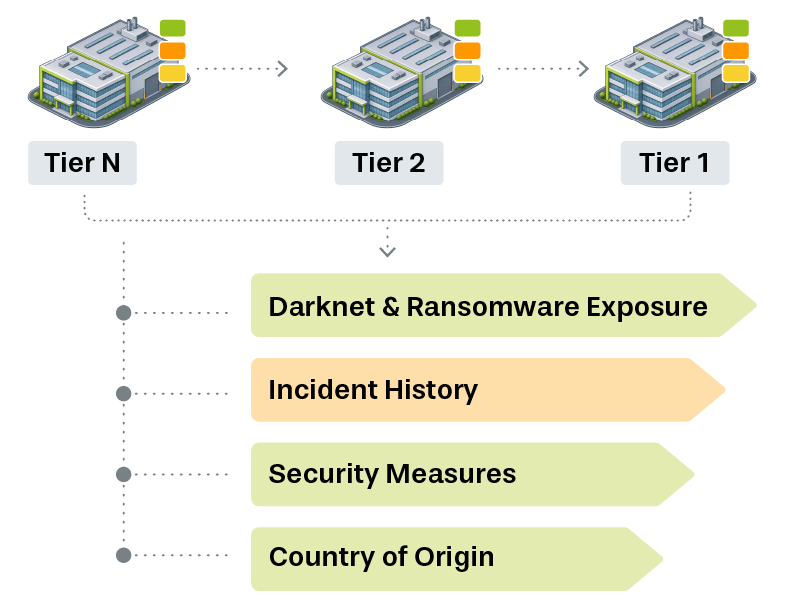
Risk-relevant data from Tier n to Tier 1
02
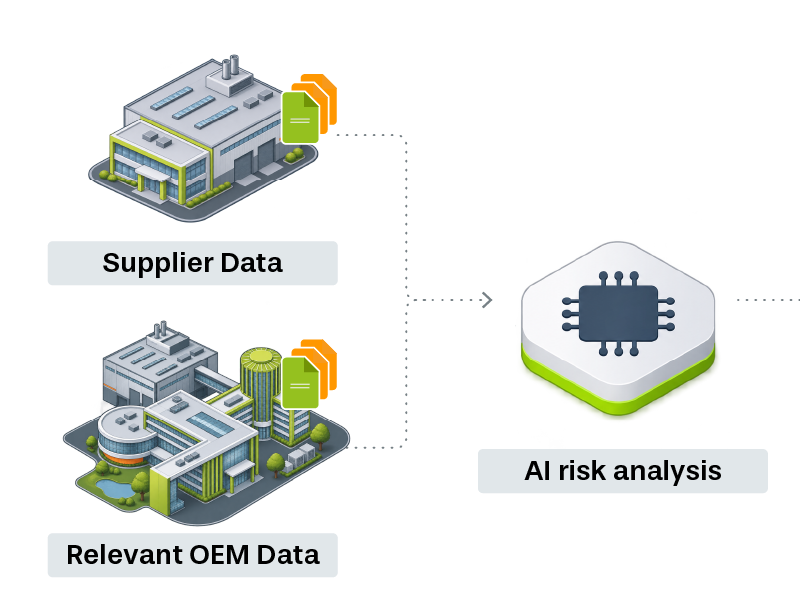
Al analyzes current supplier’s risk status
03
Graph-based risk visualisation
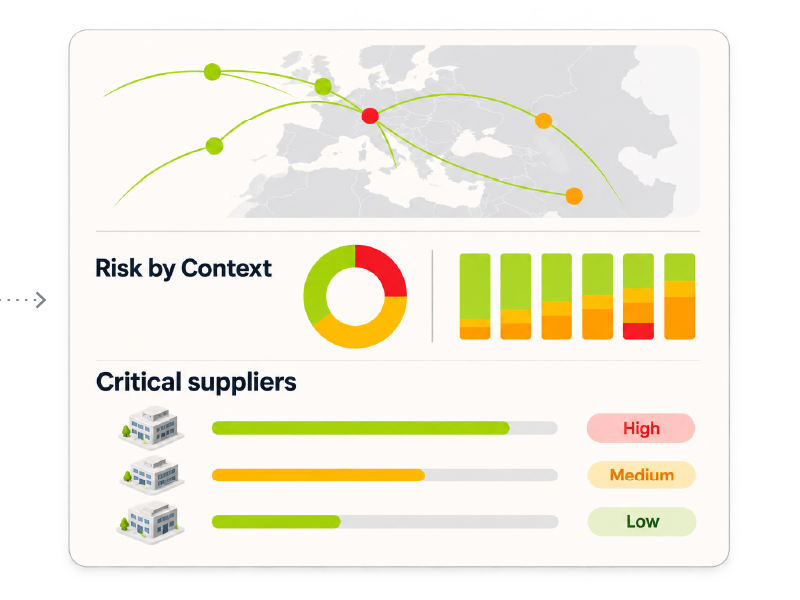
asvin’s AI-based cyber risk analysis provides an up-to-date picture of a supplier’s cyber risks and enables a more comprehensive supplier cyber risk assessment than conventional supplier management questionnaires. To do this, asvin uses context graphs to analyse a supplier’s current risk factors based on internal and external data, giving you greater visibility into cyber risks across your supply chain.
Risk by Context™ generates a risk model that considers factors such as a supplier’s exposure to the Darknet and ransomware groups, the history of known cybersecurity incidents, and the implementation of cybersecurity protection measures. It also considers characteristics such as the country of origin and current geopolitical cybersecurity risks.
BENEFITS
The benefits of asvin
01
Early detection
Early detection of supplier cyber risks
02
Ongoing re-evaluation
Ongoing re-evaluation through cyclical data updates from CTI HORIZON™ OSINT (Open Source Intelligence) data analytics
03
Targeted filtering
Targeted filtering of suppliers with high cyber risk profiles
04
Priorization of resources
Prioritization of risk management resources in critical areas
Optimize your supply chain cybersecurity risk management
Risk by Context™
supports a strategic approach that includes OSINT threats in Governance, Risk, and Compliance (GRC) solutions.
Key figures
Metrics to Create and Optimize Supply Chain Risk Management Policies
Evaluations
Assessments for better visibility into the implementation of security requirements and their controls
Analyses
Analyses for continuous review of supplier cyber dependencies
INSIGHTS & PERSPECTIVE
Understanding Today’s Cybersecurity Challenges.
Explore expert perspectives on emerging cyber threats, AI-driven security challenges, and the evolving cybersecurity landscape.
CONTACT
Let’s discuss what is truly relevant to your organisation.
In a no-obligation discussion, we’ll show you how Risk by Context™ can deliver tangible added value within your organisation
30 minutes
Teams or in person
Direct contact
with our experts
No Obligation
A conversation without commitment
CEO & Founder
Your point of contact for strategy,
cyber situational awareness and implementation