Four weeks. That’s how long it took in Berlin from the initial breach to the moment 1.4 million records appeared on the darknet.
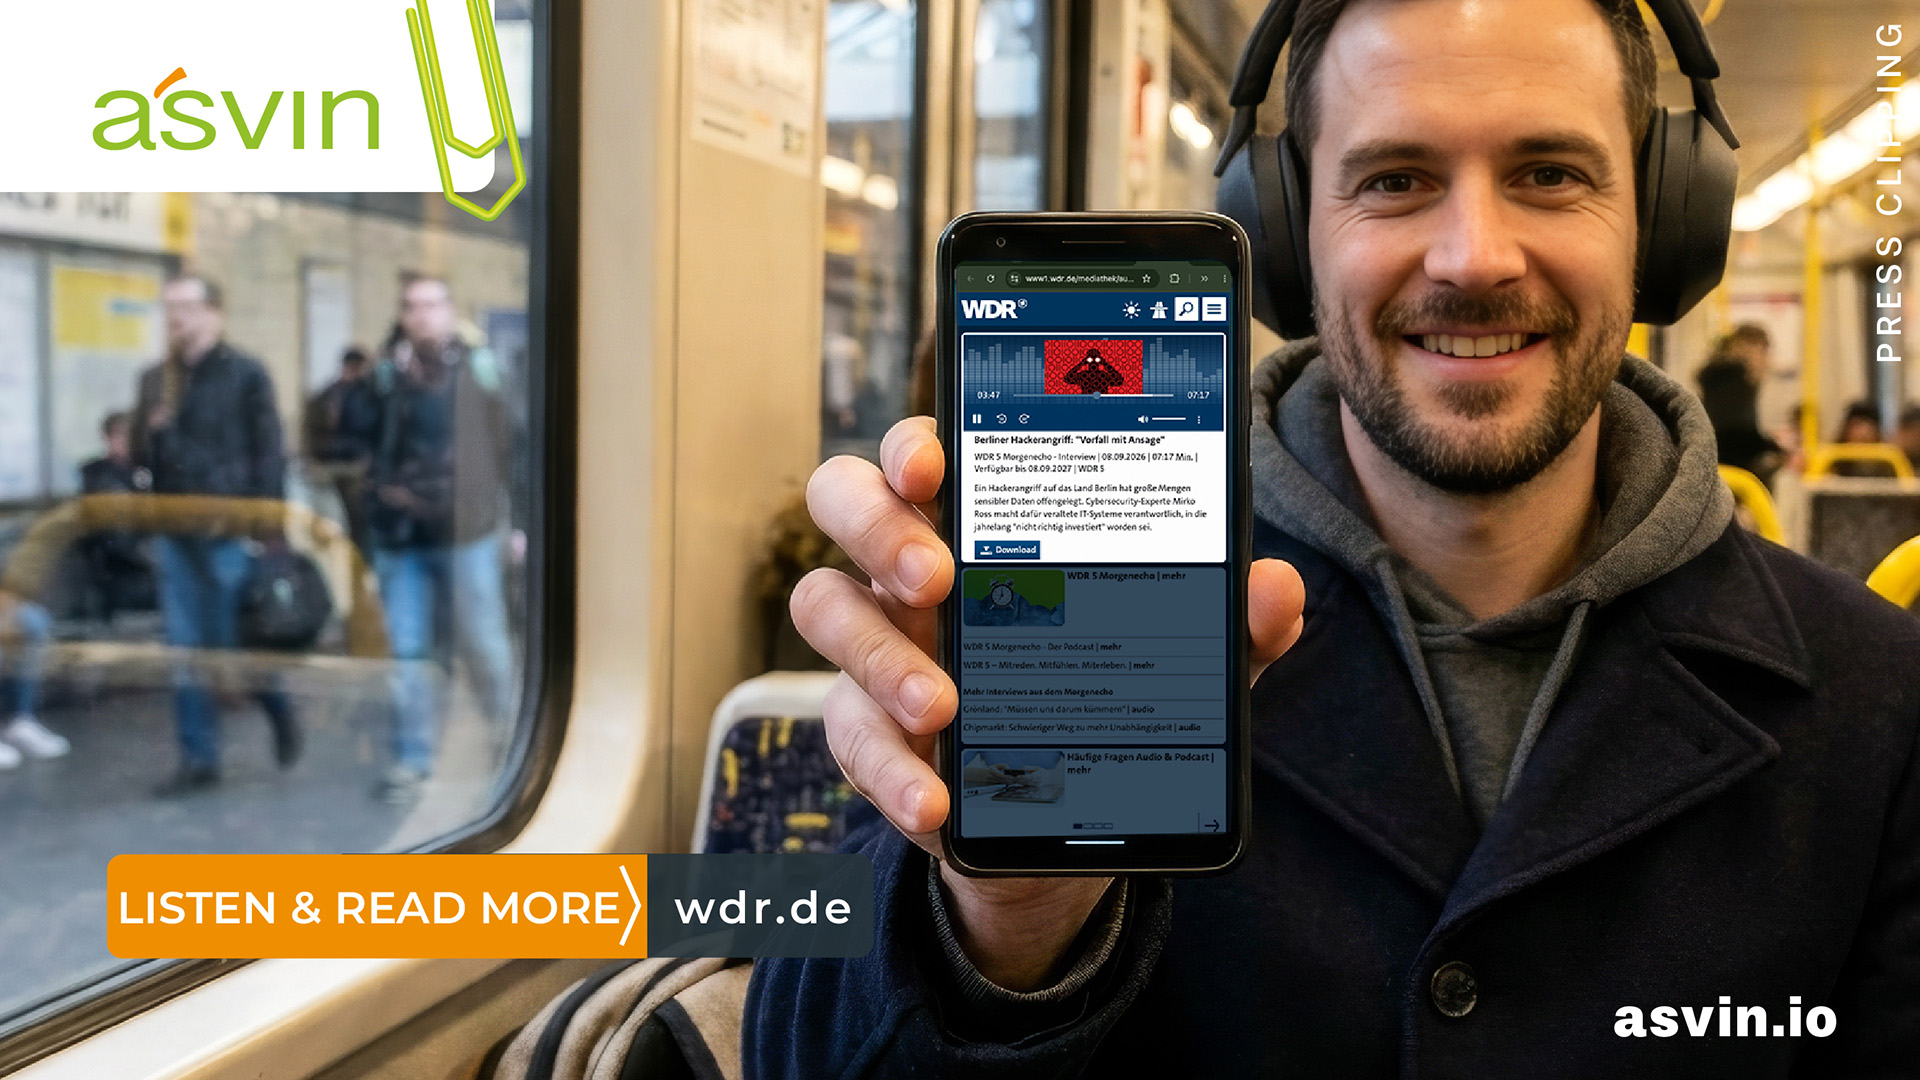
On WDR5 Morgenecho, Mirko Ross said out loud what many in the industry have been saying for years and what no one can argue away now:
“Government IT systems shouldn’t be compromisable in the first place. What was attacked here was very outdated IT. That means someone didn’t maintain these systems properly.”
In early August, attackers gained access to networks of the Berlin administration and copied data from two Senate departments.
The state refused to pay a ransom. On 4 September, the group put the data online – personnel files, performance reviews, job application documents, timesheets, contact details of public employees. The BSI considers it possible that documents relating to critical infrastructure are among them, covering hospitals, fuel depots and emergency power systems. Who exactly is affected still hasn’t been fully established.
The part that’s easy to miss
It isn’t just that old systems are easier to break into. They also leave you blind. Outdated software produces barely usable log data – so an attack is noticed late, and afterwards it’s hard to reconstruct what actually left the network.
Then there’s the timing. The data went public two weeks before the election to Berlin’s state parliament. The BSI warns about exactly this pattern: genuine documents, deliberately placed, framed in a misleading context. A maintenance failure turns into political leverage.
Four overdue consequences
- Public authorities need the same binding security requirements as companies – with proof of compliance, not self-assessment.
- Without a complete inventory of the systems and software components in use, there is no functioning patch management.
- Budgets have to fund operations, not just procurement. Security is an ongoing task, not a one-off purchase.
- Attack detection belongs in the basic setup. An incident that goes unnoticed for weeks is not bad luck
The full interview: Berliner Hackerangriff – “Vorfall mit Ansage”, WDR5 Morgenecho.

Konrad Buck
Head of Press and Media Relations
Background & Expert Access for Media
- Detailed insights into asvin’s products and technologies
- Assessments of current cyber incidents and explanations of the security landscape
- Expert commentary and background briefings — our CEO, Mirko Ross, is a recognised expert and experienced media source on the cyber threat landscape, hacktivism, regulation and the use of AI.
I speak openly, fact-based, and without PR spin. I am a former IT journalist with decades of experience in the IT and cybersecurity space, familiar with the highs and lows of the industry. Off-the-record discussions are possible upon request.