Supermarket cyberattacks: why refrigeration control systems are an easy target
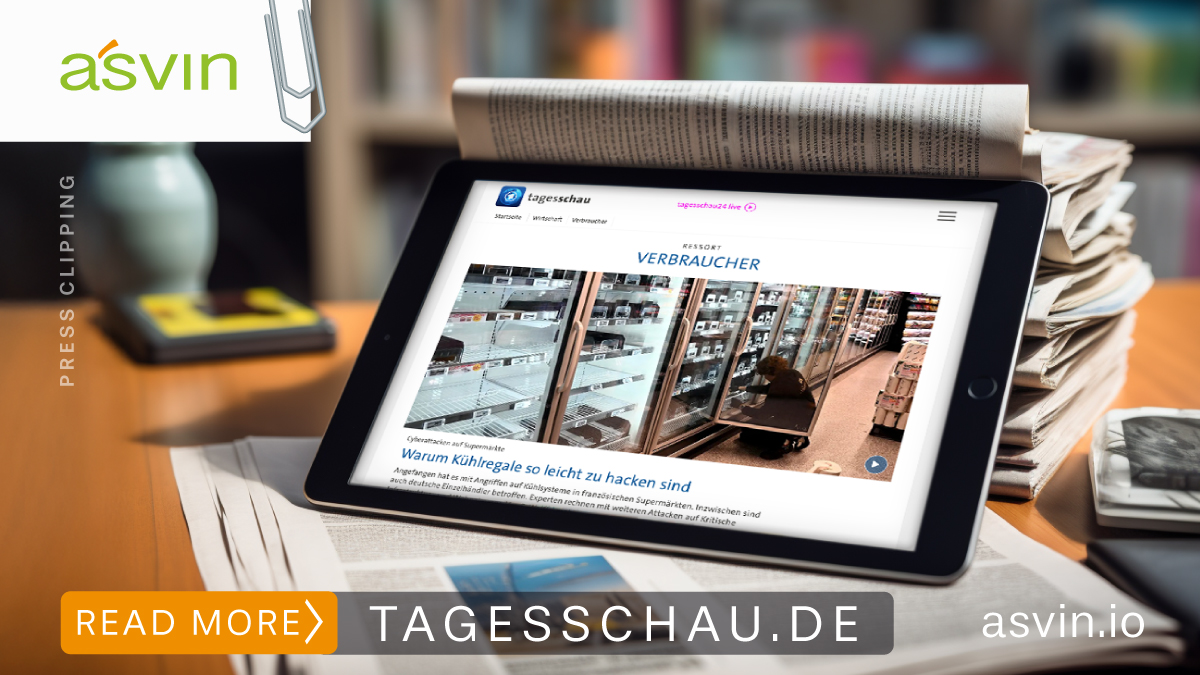
It started with the cooling systems of French supermarkets. Now German retailers have been hit as well. In an article on tagesschau.de, the ARD finance desk asks why refrigerated shelves are so easy to hack, and speaks to Mirko Ross, CEO of asvin.
He names the core problem:
“Generally speaking, these control systems are widely installed, and many of them can also be reached via the internet.” The reason is practical. The systems can be maintained remotely, so no technician needs to be on site.
Losses running into millions in France
France shows how costly this can get. “Refrigerated counters were successfully attacked across the country, and chilled goods worth several million euros were destroyed,” says the asvin CEO. He also warns: “The problem is that the affected thermostats are installed all over the world.”
The retail association speaks of “isolated cases” without significant damage. Security experts, however, see an urgent need for action. In the article, Dennis-Kenji Kipker of the Cyberintelligence Institute recommends taking the controllers off the open internet and allowing remote access only through secure connections.
The attacks don’t stop at the supermarket either. According to Mirko Ross, 1.3 million TV sets have already been hacked worldwide. His conclusion: “So these cyberattacks are hitting ever closer to home.”
Read the full article on tagesschau.de:
https://www.tagesschau.de/wirtschaft/verbraucher/hacker-kuehlsysteme-supermaerkte-100.html

Konrad Buck
Head of Press and Media Relations
Background & Expert Access for Media
- Product & technology insights – technical context, solution architecture, and real-world use cases for professional and trade media
- Expert commentary & background talks – our CEO is available as an expert source on current cybersecurity developments, threat landscapes, and the impact of AI on security and regulation
I speak openly, fact-based, and without PR spin. I am a former IT journalist with decades of experience in the IT and cybersecurity space, familiar with the highs and lows of the industry. Off-the-record discussions are possible upon request.